MDR for Splunk.
Get More from the Investment You Already Made.

Deepwatch adds 24/7 MDR expertise to your Splunk environment to improve detection, accelerate investigations, and strengthen response without replacing the platform you already rely on.
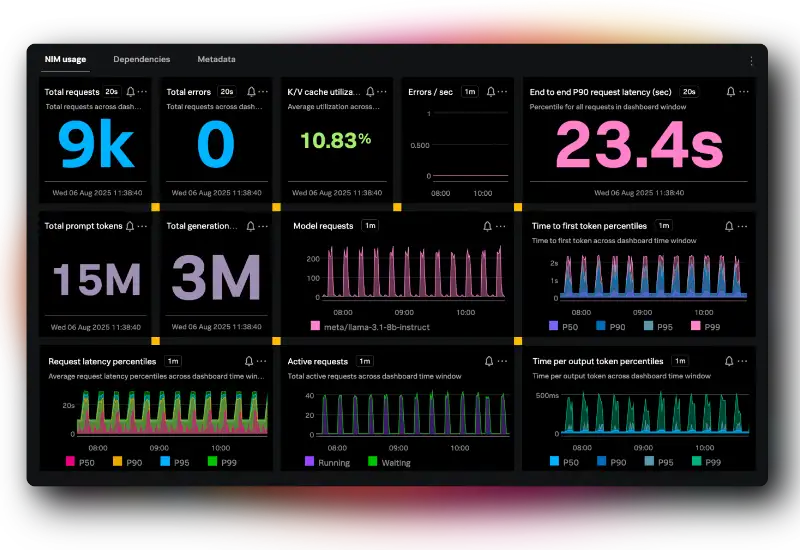
Splunk dashboard supported by Deepwatch

Trusted by leading security teams

Security outcomes

Cleaner signal.
Stronger detection.
Faster response.

Get more from Splunk with continuous detection and response coverage that helps your team prioritize threats, investigate faster, and respond without adding more operational burden.

  • Reduce alert fatigue Use contextual analysis and Dynamic Risk Scoring to surface the threats that matter most.
  • Strengthen detection coverage Continuously tune and deploy detections as threats and your environment change.
  • Accelerate investigations Combine Splunk telemetry with expert analysis and threat intelligence to investigate high-priority activity faster.
  • Extend coverage 24/7/365 Add around-the-clock monitoring without staffing additional nights, weekends, or SOC shifts.
  • Move faster on real threats Connect investigation and response workflows to turn meaningful detections into action sooner.
Deepwatch security operations dashboard

Turn Splunk signals into prioritized action

Splunk gives you the visibility. Deepwatch helps you act on it. Add the expertise, intelligence, and 24/7 coverage needed to prioritize threats, accelerate investigations, and strengthen response across your Splunk environment.

Splunk security capabilities supported by Deepwatch

Get More From Your Splunk MDR Investment

See how Deepwatch Guardian MDR is built for Splunk environments to help teams reduce operational burden, strengthen detection, and improve response without replacing the platform they already rely on.

Maximizing your Splunk investment with Deepwatch Guardian MDR

Make Splunk Work Harder for Your Security Team

Add 24/7 detection, investigation, tuning, threat hunting, and response to the Splunk environment you already use.